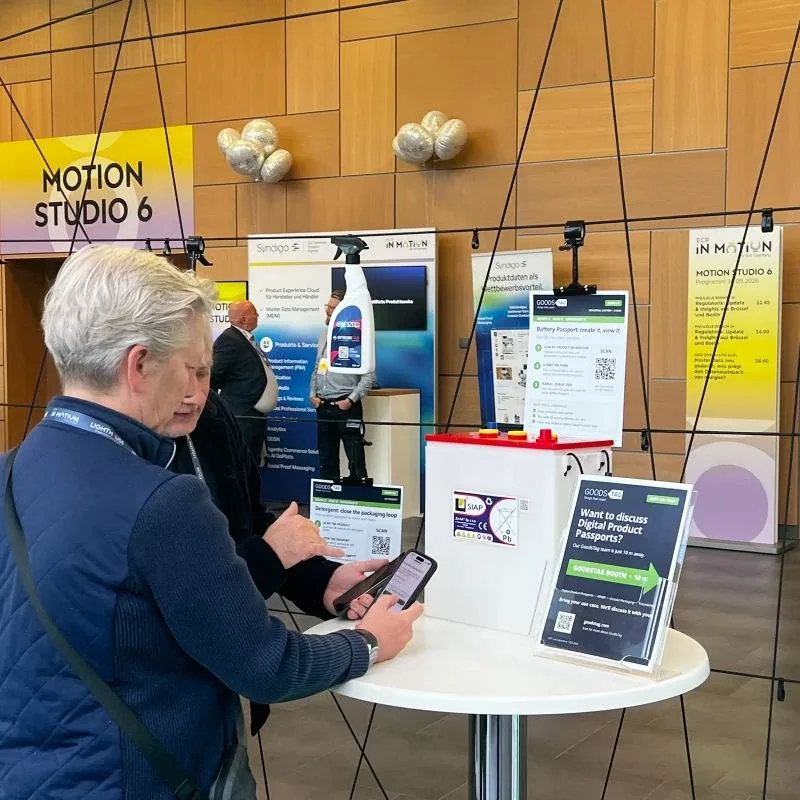

Imagine a battery manufacturer placing 50,000 industrial batteries on the European market every year. Each battery has its own digital battery passport, reached through a QR code. The manufacturer runs its own DPP platform, where product information is collected, published and updated throughout the battery's lifecycle, and it contracts an external backup provider to protect that information.
Five years later, the manufacturer goes bankrupt. Its servers are switched off, the DPP platform stops working and the website disappears. Yet thousands of batteries are still in use.
What exactly must the backup provider do? Is its job limited to keeping a copy of the passport data? Must it keep the original QR code working? Should it offer the same digital experience as the original platform? And what happens when a battery is repaired, repurposed or reaches the end of its life: can an authorised operator keep updating the passport, or is the backup now a permanent, read-only archive?
The answers shape architecture, responsibilities, data retention and pricing, and they depend on distinguishing data backup, data accessibility, operational continuity and full DPP lifecycle management. This article looks at what European legislation requires, what the technical standards address, what remains unresolved and how manufacturers should evaluate a DPP backup provider.
1. What is a "certified backup provider"?
A digital product passport backup provider is a service organisation that preserves DPP information and supports its continued availability over the period required by the applicable legislation. It protects product information against failure of the primary DPP infrastructure, discontinued software, terminated hosting contracts, loss of access to the original system, and the insolvency, liquidation or cessation of activity of the responsible economic operator. Such a service can combine several functions:
- Data preservation: keeping a reliable copy of the passport and its relevant supporting resources.
- Data replication: receiving updated information from the primary DPP system.
- Data integrity: preventing unauthorised alterations and detecting inconsistencies.
- Access management: protecting information restricted to particular stakeholders.
- Data recovery: restoring or transferring information after a system failure.
- Continuity of access: making the required information available when the primary system is no longer operational.
Not every backup service includes all the operational capabilities of the primary DPP platform. That distinction runs through the rest of this article.
Is "certified backup provider" an official EU certification?
No, not at the time of writing. The Ecodesign for Sustainable Products Regulation (ESPR), Regulation (EU) 2024/1781, defines the broader role of a digital product passport service provider (Article 2(32)): an independent natural or legal person or third party authorised by the economic operator to process the passport data.
Article 11 empowers the Commission to adopt delegated acts setting requirements for DPP service providers "and, where appropriate, a certification scheme". Those delegated acts have not been adopted. The Commission's initiative "Digital product passport - rules for service providers" (Have Your Say initiative 14382) has completed its call for evidence and public consultation, but no draft has been published. Have Your Say plans adoption in Q4 2026, while the Commission's DPP timeline lists it in 2027: expected between late 2026 and 2027, not yet adopted.
So no provider can currently be officially certified as a DPP service provider. The term "certified backup provider" describes a commercial service or an intended regulatory role. It should never be read as proof that an organisation holds an official EU certification.
2. What is legally required under the ESPR and the Battery Regulation?
Two European regulations are particularly relevant.
ESPR: Regulation (EU) 2024/1781
Article 10(4) is explicit: "The economic operator, when placing the product on the market, shall make available a back-up copy of the digital product passport through a digital product passport service provider." The independent, third-party nature of that provider follows from the definition in Article 2(32), and the Commission's official DPP FAQ (Q24) refers to a "third-party service provider".
Article 11, first paragraph, point (e), requires the passport to "remain available for the period specified in delegated acts adopted pursuant to Article 4, including after an insolvency, a liquidation or a cessation of activity in the Union of the economic operator responsible for the creation" of the passport.
Battery Regulation: Regulation (EU) 2023/1542
For battery passports, Articles 77 and 78 set the essential principles:
- Article 77(3): the passport is accessible through the QR code referred to in Article 13(6), which links to a unique identifier.
- Article 77(4): the economic operator placing the battery on the market ensures that the passport information is accurate, complete and up to date. It may authorise another operator in writing to act on its behalf.
- Article 78(c): the data are stored by the economic operator responsible under Article 77(4) or (7) "or by operators authorised to act on their behalf".
- Article 78(d): those authorised operators may not sell, re-use or process the data beyond what is necessary to provide the service.
- Article 78(e): the passport remains available even after the responsible operator ceases to exist or ceases its activity in the Union.
- Article 78(f): rights to access, introduce, modify or update information are restricted according to the access rights.
The Battery Regulation requires continued availability of the passport, but it does not state that a backup provider must reproduce every operational function of the original DPP system. How the ESPR's third-party backup obligation applies to battery passports governed by sector-specific legislation also needs careful legal interpretation. For manufacturers, an external backup is a practical way to address continuity risk, but its functional scope has to be defined. If you are unsure who carries which obligation, see our overview of who is responsible for the digital product passport.
3. The four levels of DPP backup services
It helps to distinguish four levels of functionality.
| Service level | Principal function |
|---|---|
| Level 1 - Data preservation | Store a recoverable copy of the passport |
| Level 2 - Accessible backup | Let authorised users retrieve backed-up information |
| Level 3 - Operational failover | Keep access through identifiers, endpoints or QR code recovery when the primary system fails |
| Level 4 - Lifecycle continuity | Support authorised changes and ongoing DPP operations after a transfer of responsibility |
These levels describe possible service architectures. They are not official EU certification classes or legally prescribed categories.
Level 1: Data preservation
The provider stores the passport datasets and supporting information, while the primary platform stays responsible for publication, access, QR code resolution and updates. If the primary system fails, the backup restores the data on another platform. Like classic backup-as-a-service, it protects data but does not give stakeholders immediate access.
Level 2: Accessible backup
The backed-up information is retrievable, for example through an API that lets an authorised user or another DPP application fetch the structured dataset, without the original user interface or application.
Level 3: Operational failover
The provider makes the required information available when the original platform goes down, through backup endpoints, identifier resolution or routing changes. This matters most when a product carries a QR code that cannot practically be replaced.
Level 4: Lifecycle continuity
The provider, or a successor operator using its infrastructure, also supports authorised updates after the original platform or responsible operator has disappeared: new versions, lifecycle events and transfers of responsibility. At this level, the service resembles a full DPP platform.
A key procurement question is therefore whether the backup provider offers preservation only, continuity of access, or complete lifecycle continuity.
4. Must a backup provider also operate a QR code resolver?
A battery passport must be accessible through the QR code linked to its unique identifier (Article 77(3) of the Battery Regulation). However, the current legislation contains no general requirement that every backup provider operate its own QR code resolver.
That does not mean resolution can be ignored. The legal requirement concerns passport accessibility; the technical responsibility for achieving it can be split between different components and operators.
How QR code resolution normally works
- The battery carries a QR code containing or linking to a persistent product identifier.
- The identifier is resolved through a digital service.
- The resolver directs the user or application to the relevant DPP resource.
- The DPP system returns the requested information according to the user's access rights.
The resolver and the data store can be separate components. A manufacturer might use a GS1 Digital Link resolver while hosting the passport data in another application.
What happens if the primary DPP platform disappears?
If the QR code points to a resolver run by the manufacturer and its website and DNS disappear, the code may lead nowhere. The backup provider may hold the complete dataset, but users cannot find it.
Three possible technical approaches
Option A - Independent resolver. A resolver that does not depend on the manufacturer's infrastructure routes requests to the primary platform normally and to an alternative source when necessary.
Option B - Backup provider with resolution. The backup provider also offers identifier resolution or a compatible endpoint that directs users to the backup when the primary system fails.
Option C - Registry-supported discovery and recovery. The EU DPP Registry holds identifiers and registration information, and under Commission Implementing Regulation (EU) 2026/1778 the Commission checks the link to the back-up copy hosted by a DPP service provider at registration (Article 8(7)(e)). But the Registry is not a replacement for a manufacturer's QR code resolver; a practical recovery mechanism still has to be implemented. We explain the Registry checks in detail in what the EU DPP Registry validates.
So is a resolver mandatory for the backup provider?
Not as a separate built-in feature under the rules currently in force. But if a backup provider promises that the original QR code journey keeps working after the primary system disappears, it must provide or rely on a working resolution and failover mechanism, and explain exactly how it works. Otherwise, a claim to guarantee DPP continuity may be misleading.
5. Must the backup provider reproduce the original DPP website?
Not necessarily. A passport consists of structured, machine-readable information and associated resources. A manufacturer may present it through a rich multilingual website, but the regulatory objective is that the passport information stays available under the relevant technical and access requirements, not that every aspect of the website survives. Two approaches are possible:
- Preserve the complete user experience: the backup reproduces the original presentation. Attractive for users, but more complex.
- Preserve the data and provide an alternative presentation: when activated, the backup shows the required information through a standardised interface. Simpler and often cheaper, provided all access and presentation requirements are met.
A manufacturer should ask whether the backup contract covers the original website, the underlying data, linked documents, or a combination of these.
6. Can the backup provider modify or update passport information?
Receiving and preserving updates from the primary DPP system is different from being authorised to create or modify passport information independently.
During normal operation
Under Article 77(4), the economic operator placing the battery on the market remains responsible for keeping the passport accurate, complete and up to date. When the manufacturer corrects a battery attribute, the primary platform records the change, transmits the revised dataset to the backup, and the backup verifies, stores and versions it. The backup provider performs technical synchronisation; it does not decide whether the new information is correct.
Can the provider edit the data itself?
Not simply because it holds a backup copy. Article 78(f) restricts the rights to introduce, modify or update information according to the access rights, and Article 78(d) limits authorised operators to processing that is necessary for their service. A backup provider does not become authorised to change product data by default; editing rights require a lawful authorisation, such as the written authorisation foreseen in Article 77(4).
What happens after the manufacturer disappears?
Batteries outlive manufacturers, and information such as condition, lifecycle status and second-life activities keeps evolving. A read-only archive preserves the last known version but cannot accept new lifecycle information.
Hosting the backup does not automatically transfer the manufacturer's legal responsibility to the backup provider. The system must distinguish between preserving existing information and letting a legally authorised successor or other relevant operator add new information. The post-insolvency operating model remains an important contractual and legal issue.
7. What happens when a new economic operator takes responsibility?
The Battery Regulation already covers certain lifecycle changes. Under Article 77(7), when a battery is prepared for re-use, prepared for repurposing, repurposed or remanufactured, responsibility passes to the operator placing it on the market or putting it into service, and a new battery passport must be created and linked to the passport or passports of the original battery. When the battery becomes waste, responsibility transfers either to the producer or to the producer responsibility organisation or the waste management operator. Under Article 77(8), the passport ceases to exist after the battery has been recycled.
For the backup provider, this creates several possible responsibilities:
- Preservation of the original passport: the original record must remain available where required.
- Data portability: information may need to be transferred to another authorised DPP operator.
- Continuity of identification: identifiers and links between related passports must remain meaningful.
- Successor access: a new responsible operator may need access to information to meet its obligations.
None of this requires the backup provider to run the new passport: it may export the original data to the successor's DPP platform, or offer lifecycle management as an additional service where the legal authority, access controls and contracts are in place. Several of these hand-over situations are still unclear in practice; we list them in the open questions on the EU battery passport for 2027.
8. Read-only backup or read-write DPP platform: what should companies choose?
The answer depends on the continuity service being purchased.
| Functionality | Read-only backup | Full continuity service |
|---|---|---|
| Preserve passport data | Yes | Yes |
| Receive updates from the primary system | Typically yes | Yes |
| Preserve historical versions | Recommended | Recommended |
| Make stored information retrievable | Needed for an accessible backup | Yes |
| Present passport information to users | Optional separate capability | Typically included |
| QR code resolution failover | Separate arrangement unless included | Should be addressed |
| Independently edit product attributes | No | Only with lawful authorisation |
| Allow authorised successor updates | Generally needs another platform | Can be supported |
| Manage new lifecycle events | Not inherently | Can be supported |
| Create new passports after repurposing | No | Possible with the appropriate role and authority |
| Synchronise Registry information | Not inherently | May be included when authorised |
This is an architectural comparison, not a statement that every feature in the right-hand column is legally mandatory for all backup providers.
The practical recommendation
A read-only preservation service can be a sound building block. But a manufacturer relying on it must separately make sure that:
- the backup can actually be retrieved;
- the original product identifiers remain usable;
- the information remains accessible to authorised stakeholders;
- a lawful mechanism exists for future lifecycle updates where necessary.
For long-lived batteries, a backup strategy that only stores files, without a recovery and successor-access plan, is incomplete.
9. What does EN 18221:2026 cover?
The European standard EN 18221:2026, Digital product passport - Data storage, archiving, and persistence, is particularly relevant. Commission Implementing Decision (EU) 2026/1736 of 14 July 2026 cites it in the Official Journal without restriction, together with EN 18216, EN 18219, EN 18220, EN 18222 and EN 18223. Citation gives a presumption of conformity only for the parts of ESPR Articles 10 and 11 that the standard covers.
According to the published catalogue description, its scope includes:
- Data storage of passport information;
- Archiving of historical passport information;
- Persistence, so that passport data remains available over time;
- Replication between economic operators and back-up operators;
- Data lifetime rules for how long data must remain available.
It is an important technical basis for backup infrastructure. But the full normative text is a paid document, and the public scope description does not establish, for example, that every backup provider must offer a resolver or an editing interface. EN 18221 should be read together with the other DPP standards on identifiers, data carriers, interoperability and APIs, and it is not a business contract, a funding mechanism or a certification scheme.
10. What infrastructure should a DPP backup provider operate?
A production-ready service should address several technical layers:
- Secure storage: structured DPP data and, depending on scope, documents, declarations, metadata and passport versions. A backup that only holds links to files hosted by the manufacturer becomes useless when those files disappear.
- Reliable replication: API-based, scheduled or event-driven, with failures detected and corrected. A useful metric is the maximum acceptable gap between the latest primary data and the latest preserved backup.
- Integrity and auditability: checksums, controlled version records and audit logs show which version was preserved and reveal unauthorised changes.
- Access control: public and restricted information stay separated. A manufacturer's disappearance does not justify publishing confidential battery data.
- Recovery and failover: a defined procedure, including endpoints, credentials and identifier-resolution arrangements.
- Data portability: the manufacturer can move to another compatible provider; the backup must not create new vendor lock-in.
- Operational resilience: protection against infrastructure failures and wider hosting disruptions. Redundancy does not guarantee legal or financial continuity, but it is an essential component.
11. How quickly must a backup provider restore access?
At the time of the last review, no EU rule prescribed a single recovery time for every DPP backup service. The legal framework sets requirements for accessibility and continued availability; detailed operational requirements may come from technical standards, the future service provider rules and contracts.
Manufacturers should distinguish two service-level concepts:
- Recovery Time Objective (RTO): how long the provider may take to restore access after a failure.
- Recovery Point Objective (RPO): how much recent data may be lost because it had not yet been replicated.
A provider might contractually offer a four-hour recovery and a one-hour replication objective: negotiated commitments, not legal thresholds. Recovery after several weeks is worth far less than rapid failover, especially for batteries whose safety and dismantling information is needed in the field.
12. How long must the data be retained?
There is no single retention period for all digital product passports. Under ESPR Article 9(2)(i), the product-specific delegated acts set the availability period, which must be "at least equal to the expected lifetime of a specific product". For battery passports, Article 77(8) of the Battery Regulation states that the passport ceases to exist after the battery has been recycled.
So the service duration cannot simply be derived from the manufacturing date. A battery placed on the market in 2027 might serve eight years in its first application and then be repurposed; retention must follow the lifecycle rules, any new linked passport and the operators involved.
What about annual subscriptions?
A one-year subscription does not mean one year of passport availability. The contractual billing period, the active service period and the regulatory preservation period are different things, and a responsible pricing model explains how they interact. Ending a subscription does not end the required availability of passports for products already on the market.
13. The insolvency problem: who pays if the manufacturer disappears?
A manufacturer creates 100,000 battery passports over several years, pays an annual fee to a backup provider, then goes bankrupt. The batteries stay in use and their passports must remain available, but nobody pays any more. Must the backup provider keep hosting for free?
European legislation does not establish a mechanism requiring a commercial backup provider to finance unpaid hosting indefinitely after a customer's insolvency. It sets continuity obligations, but the funding of long-term costs must be organised, and a plain annual subscription leaves a gap between the payment period and the passports' legally relevant lifetime.
Possible financing mechanisms
- Prepaid preservation: the manufacturer pays upfront for an agreed long-term storage period.
- Continuity reserve: part of the service fee finances a reserve to maintain essential services after customer failure.
- Escrow arrangement: funds are held under a legally protected arrangement for defined future preservation obligations.
- Hybrid model: active processing and updates are paid by subscription, while core preservation is financed separately.
- Transfer to a successor: another responsible economic operator takes over the service obligations where legally and operationally appropriate.
None of these is imposed as a mandatory EU pricing model. Manufacturers should examine a provider's actual continuity arrangements instead of assuming that a one-year storage contract guarantees decades of preservation.
14. What if the backup provider itself goes bankrupt?
A backup that protects against the primary operator disappearing must also plan for its own disappearance. Key safeguards:
- exportable and interoperable passport data;
- clear ownership and access arrangements;
- transfer procedures to a replacement provider;
- preservation of the necessary identifiers and metadata;
- arrangements for transferring encryption keys or keeping access recoverable;
- disaster recovery and continuity plans;
- contractual provisions addressing provider failure.
Ask whether any long-term preservation funds would stay protected if the provider became insolvent: money set aside internally may not offer the protection of an independent arrangement. This is one reason the future service provider rules on resilience may matter commercially.
15. Can manufacturers self-host the primary DPP and provide their own backup?
Under Article 78(c), the responsible economic operator may store battery passport data itself, so a manufacturer can run its own primary DPP and technical backups. That does not solve long-term independence: if all systems, domains, credentials and cloud subscriptions belong to the same company, its insolvency can take down both the primary passport and its backup. For DPPs governed directly by the ESPR, Article 10(4) requires the back-up copy to be made available through a DPP service provider, which the Commission FAQ describes as a third party. For battery passports, the interaction with the sector-specific rules should be assessed case by case.
A practical architecture
To keep control of its primary DPP, a manufacturer could combine:
- Primary infrastructure: its internally managed DPP system.
- Independent backup infrastructure: a third-party service holding copies of the necessary information.
- Persistent identification: an identifier and resolver arrangement designed to survive failure of the primary environment.
- Contractual continuity: a mechanism that preserves access when the manufacturer no longer exists.
16. What role does the EU DPP Registry play?
The EU Digital Product Passport Registry went live on 20 July 2026. Commission Implementing Regulation (EU) 2026/1778 was adopted on 16 July 2026, published in the Official Journal on 17 July 2026 and entered into force on 6 August 2026. The Registry is central to the European DPP architecture, but it is not the repository for complete passports.
The Implementing Regulation:
- governs the verification of economic operators (Article 4);
- governs the registration of passports (Article 8);
- provides for a list of verified DPP service providers (Article 3(f));
- has the Commission check, where applicable, the link to the back-up copy hosted by a DPP service provider (Article 8(7)(e)).
It sets no procedure for certifying service providers, and recital 16 makes clear that the Registry's checks are not proof of compliance. A backup link recorded in the Registry should also not be confused with a guarantee that a scanned QR code will fail over to the backup in every failure scenario. The operational recovery mechanism still has to be designed.
17. Is formal certification of backup providers mandatory today?
No. The ESPR empowers the Commission to set requirements for DPP service providers by delegated act and, where appropriate, a certification scheme. The consultations are complete, but at the time of the last review the delegated act had not been adopted and no certification scheme existed. Several concepts must therefore be kept apart:
- Identity verification: establishing that an operator or service provider is who it claims to be.
- Technical conformity: demonstrating that a system implements particular standards or passes defined interoperability tests. Independent testing, such as the BatteryPass-Ready compliance testing, belongs here.
- Operational assurance: evidence of resilience, security, continuity and contractual processes.
- Formal regulatory certification: completing a certification procedure established under EU law, if and when one exists.
These are not interchangeable. Strong technical credentials are not an official EU certification, which does not yet exist, and appearing on the Registry's list of verified service providers is not the same as passing a service provider certification scheme.
What might future requirements address?
Possible subjects include service continuity, security, interoperability, data availability, governance and certification. Their content can only be assessed once the delegated act is adopted, expected between late 2026 and 2027. Businesses should choose providers that can adapt to these developments.
18. What questions remain genuinely open?
| Question | Current position |
|---|---|
| Must every backup provider operate a QR code resolver? | No explicit general requirement; continuity of access must nevertheless be ensured |
| Must a backup reproduce the original passport website? | Not specified as such |
| Must a backup provider support independent editing of passport data? | No editing authority arises from the backup role alone |
| Must updates from the primary system be replicated? | A current, usable backup needs an appropriate synchronisation approach |
| Who can update a passport after manufacturer insolvency? | Depends on the legally authorised actor and the lifecycle rules |
| Does the provider need full lifecycle-management functionality? | Not established for a backup-only service |
| How quickly must a backup restore access? | To be defined in contracts and technical requirements |
| Who pays after the customer becomes insolvent? | No EU funding mechanism established |
| Must the primary and backup providers be separate? | ESPR requires a third-party service provider; detailed independence rules are pending |
| What happens if the backup provider disappears? | Requires contractual and technical continuity planning |
| Will official provider certification become mandatory? | Delegated act and possible certification scheme not yet adopted |
| How should backups evolve when a battery receives a new passport? | Original and new passports must be managed consistently with Article 77(7) |
Some will be clarified by the future delegated act and standards; others will remain commercial and architectural decisions.
19. What should companies require from their backup provider?
Before selecting a service, get written answers to these questions:
- Data coverage: exactly what is backed up? Structured data, supporting documents, versions and all necessary metadata?
- Synchronisation: how are changes received from the primary system, and how are failed replications detected and corrected?
- Retrieval: can another system retrieve the data independently of the original DPP application? Are standardised interfaces available?
- QR code continuity: what happens when the original resolver, domain or hosting disappears, and how do users still reach the information?
- Access rights: how are restricted data and authorised users handled in normal operation and in emergency recovery?
- Editing and lifecycle events: is the service read-only, or can it support authorised successor operations? Which functions need an additional agreement or platform?
- Retention and pricing: how long is information preserved, and what happens financially if the manufacturer stops paying or becomes insolvent?
- Provider failure: how can the data be moved to a replacement provider, and can the recovery procedure be tested?
- Regulatory conformity: which standards have been implemented and tested? Does the provider clearly distinguish technical conformance from formal EU certification?
A good provider answers these without falling back on "your data is safe in the cloud".
20. Our recommendation: separate preservation, accessibility and lifecycle management
The most robust approach treats DPP continuity as three related but distinct responsibilities:
- Preservation: maintain a reliable copy of the required information.
- Accessibility: ensure authorised users can still retrieve it when the original system is unavailable.
- Lifecycle management: let legally authorised operators add new information and manage product events.
A backup-only provider need not deliver the third function itself, but the overall architecture must cover all applicable requirements. For long-lived products such as industrial and EV batteries, do not assume the original company, software and hosting will last forever, and do not pay for a complex duplicate platform when simpler, interoperable preservation and recovery services are enough.
The right solution is not necessarily the most feature-rich backup provider. It is the combination of services that reliably preserves the legally required information, and access to it, throughout the product's relevant lifetime.
21. Conclusion: a backup must be more than a stored file
Several different responsibilities are often grouped under the label "certified backup provider". The essential legal objective is continued availability of the required passport information, which may take secure storage, replication, retrieval, continuity of identifier resolution and arrangements for authorised successors.
Not every backup provider has to run a full DPP platform. But a static file stored without a plan for future access, updates, changes of responsibility and provider failure does not deliver credible long-term continuity. With the service provider rules and a possible certification scheme still to come, evaluate providers not only on storage price, but on the architecture, contracts and technical capabilities behind their continuity promise.
How GoodsTag helps: the GoodsTag Certified Backup Provider service
GoodsTag offers a backup service for digital product passports under the name GoodsTag Certified Backup Provider service, for manufacturers, brands and DPP solution providers that want a dedicated, independent backup within their DPP architecture. To be clear: "Certified" is the name of the service, not an official EU certification. No EU certification scheme for DPP service providers exists yet, and we follow the Commission's work on the future rules closely.
To discuss technical scope, integration with your primary DPP platform, QR code continuity, retention arrangements and pricing, contact GoodsTag through our contact form.
Official sources
- Regulation (EU) 2024/1781 (ESPR), Articles 2(32), 9, 10 and 11
- Regulation (EU) 2023/1542 (Battery Regulation), Articles 13, 77 and 78
- Commission Implementing Regulation (EU) 2026/1778 (DPP Registry)
- Commission Implementing Decision (EU) 2026/1736 (harmonised DPP standards, including EN 18221:2026)
- European Commission: Digital product passport FAQ
- European Commission: Digital product passport - rules for service providers (initiative 14382)
Last regulatory review: 10 October 2026. The article distinguishes established legal requirements from technical recommendations, optional service capabilities and matters awaiting regulatory clarification. It is not legal advice.